Compliance
ISO 27001 certification, minus the consultant bill
ISO 27001 is the certification enterprise and European buyers ask for by name. Mycroft maps the controls, gathers the evidence and keeps your ISMS current between audits, so certification does not turn into a yearly fire drill.
Trusted by


Why ISO 27001 matters to you
ISO 27001 provides a globally recognized framework for managing information security risks and protecting sensitive data.

Global credibility
ISO 27001 certification demonstrates strong security practices to customers and partners worldwide.

Structured risk management
Identify, assess, and mitigate information security risks systematically.

Enterprise readiness
Certification is often required to work with large organizations and international clients.
Free. Email only, no sales call
Not ready to talk to us yet?
Start with our security audit checklist and find out where you actually stand before anyone tries to sell you anything.
Get your audit checklist

5 minute read
Features
Mycroft’s AI platform solutions for ISO 27001
A unified platform designed to operationalize ISO 27001 requirements without adding internal workload.
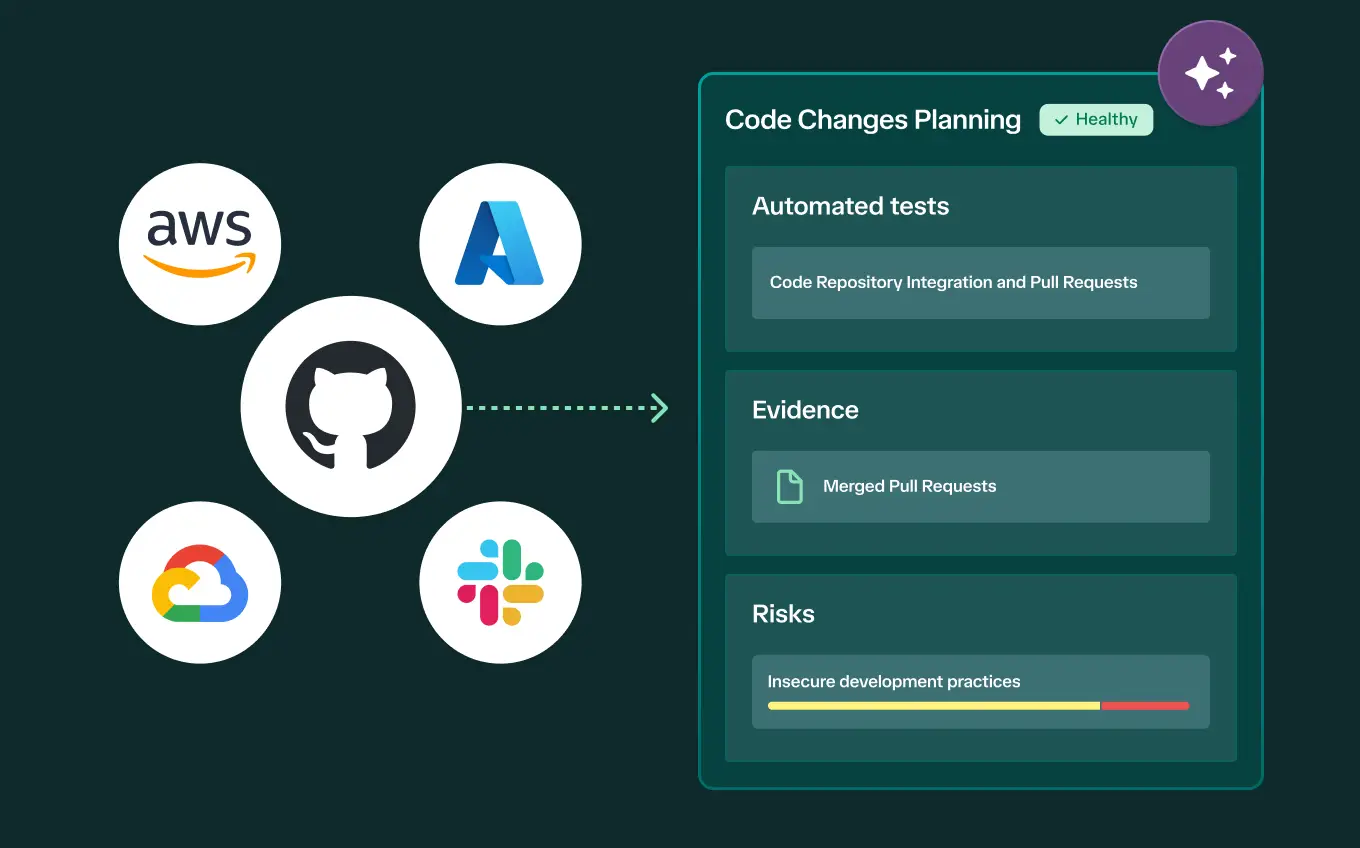
Custom controls
Create and manage custom security controls tailored to your organization’s operational, regulatory, and customer requirements while simplifying compliance mapping across frameworks.
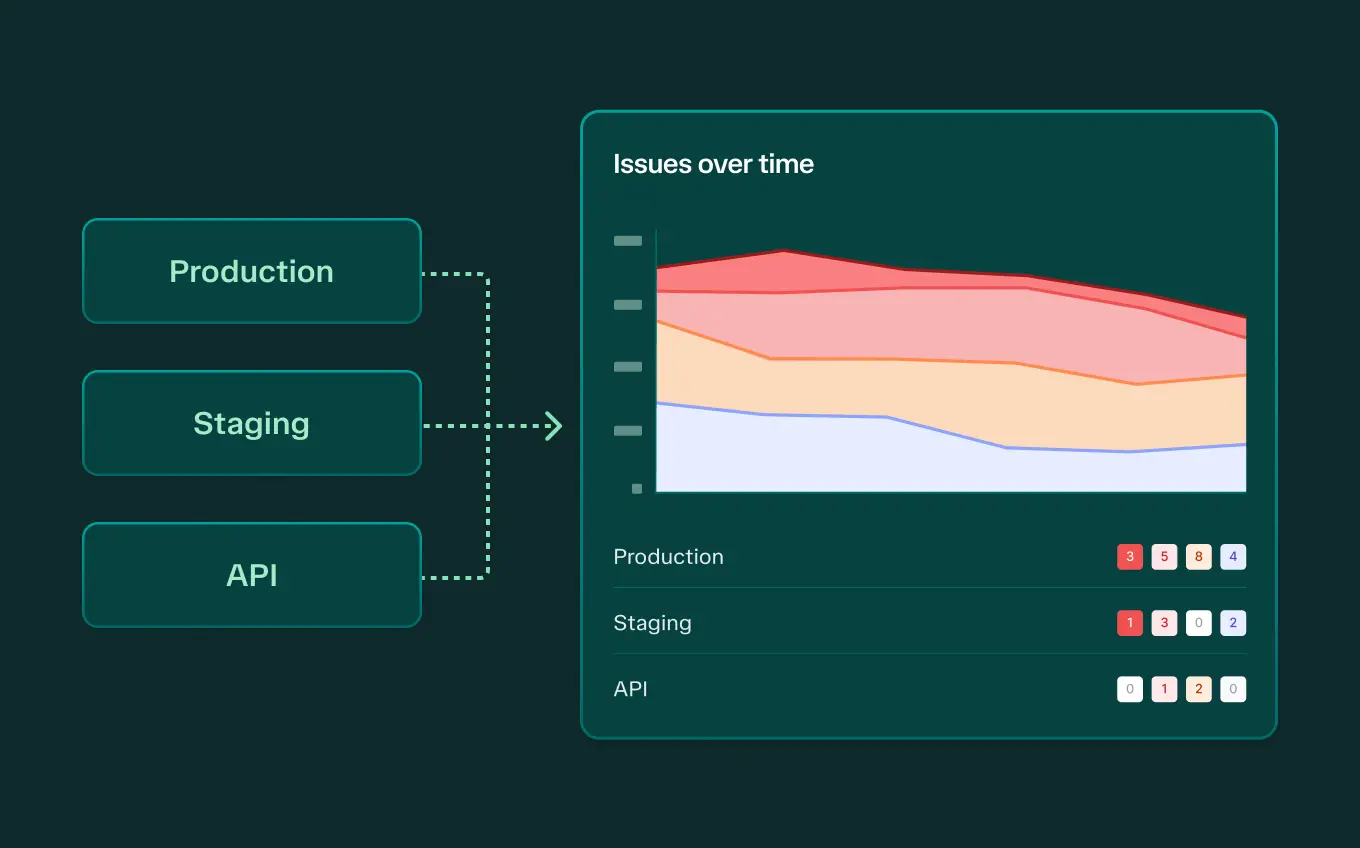
App secruity
Improve application security by identifying vulnerabilities, monitoring configurations, and supporting secure development practices across your software environment.
Support and live chat
Access live support and hands-on guidance from compliance and security specialists to resolve issues quickly and keep your compliance program moving forward.
Additional features for ISO 27001
Integrated capabilities to support your information security management system.
Risk assessment
Identify and prioritize security risks
Cloud security
Protect cloud infrastructure
and services
and services
Risk insight reports
Delivers reports prioritizing risks, actioned by Mycroft Agents
Security questionnaires
Streamline vendor security assessments
AI policy generator
Produce and iterate clear, auditable policy documents
Automatic evidence collection
Gathers and stores evidence
Third party risk management
Assess and monitor vendor risk
Security training
Interactive employee cybersecurity education
Policy center
Centralized, versioned compliance policies
Client Testimonial
“
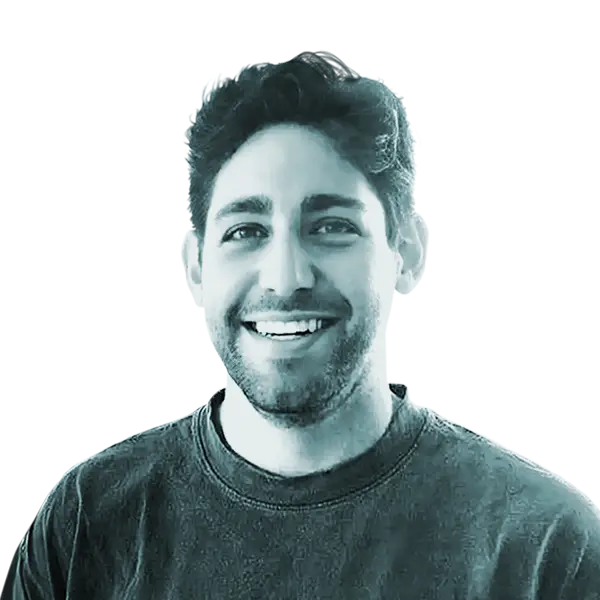
Mycroft’s 5-in-1 platform seamlessly consolidated our entire security stack, eliminating the need for multiple point solutions and endless checklists.”
Adam Cohen
CEO of WEAVE
Frequently asked questions
Answers that help customers with ISO 27001 compliance
What is ISO 27001?
Who needs ISO 27001 certification?
What is an ISMS?
How long does ISO 27001 certification take?
How does Mycroft help with ISO 27001?
We turn the compliance nightmare into a dream
Talk to us